

JWT Decoder & Encoder
Tokens and secrets stay in your browser. Still, avoid pasting live production tokens into any website.
Header
Payload
Signature valid
Signature does not match
Only HMAC (HS) signatures can be checked with a secret. RS and ES tokens need the public key.
Signed token


JWT Decoder & Encoder
A JSON Web Token (JWT) is three Base64URL parts: a header, a payload of claims, and a signature. Paste a token to read the header and payload, with timestamps such as iat and exp shown as dates and a clear warning if it has expired. With the secret you can verify HS256, HS384 and HS512 signatures, or build and sign a new token for testing. Everything runs in your browser with the Web Crypto API.
How to use JWT Decoder & Encoder
- Paste the token.
- Read the decoded header and payload and the expiry status.
- To verify an HMAC-signed token, enter the secret.
- To create a token, edit the header, payload and secret on the encoder side and copy the signed token.
When it comes in handy
- Debugging login and API authentication problems.
- Checking which claims and expiry a token carries.
- Generating test tokens for development.
Frequently asked questions
Is a JWT encrypted?
No. A signed JWT is only encoded, so anyone with the token can read the payload. Never put passwords or secrets in it.
Can it verify RS256 tokens?
Not at the moment. RS256 and ES256 tokens are decoded, but verifying them needs the issuer's public key; check them in your backend library.
Should I paste production tokens here?
The token stays in your browser, but a live token is a credential. Prefer expired or test tokens on any website.
Related guides
-
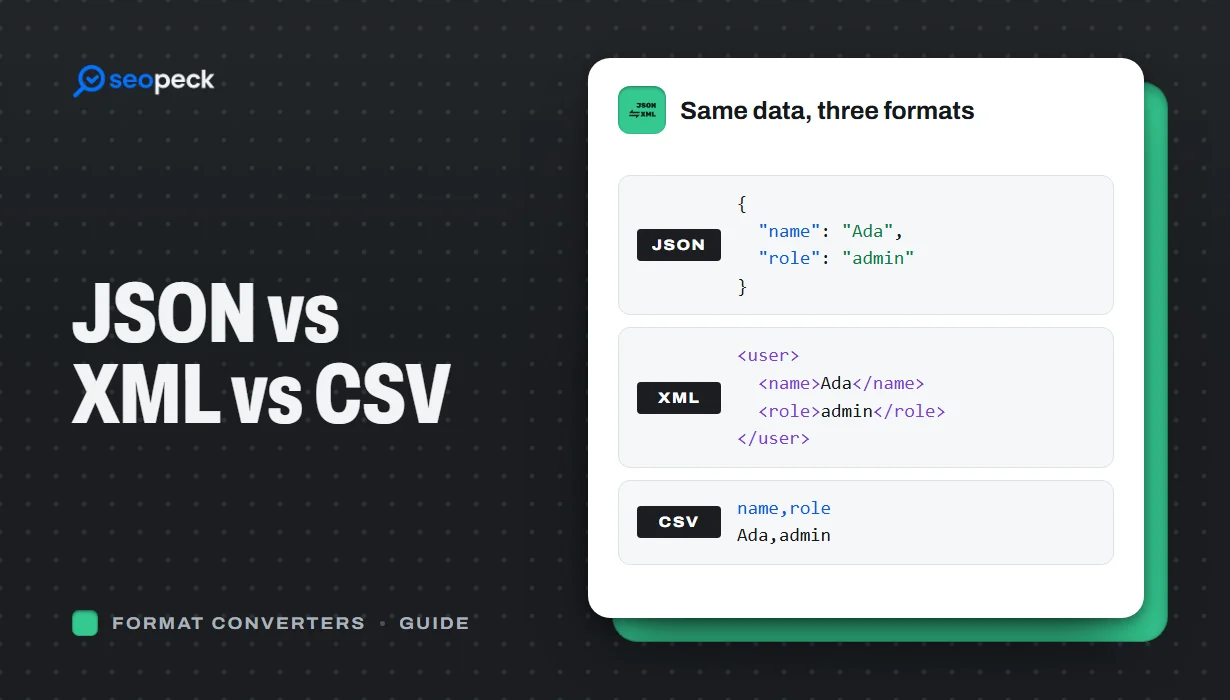 JSON vs XML vs CSV: Choosing the Right Data Format for Your Project
JSON, XML and CSV each solve a different problem. Here is how to pick the right one, plus tools to convert and validate between them.
-
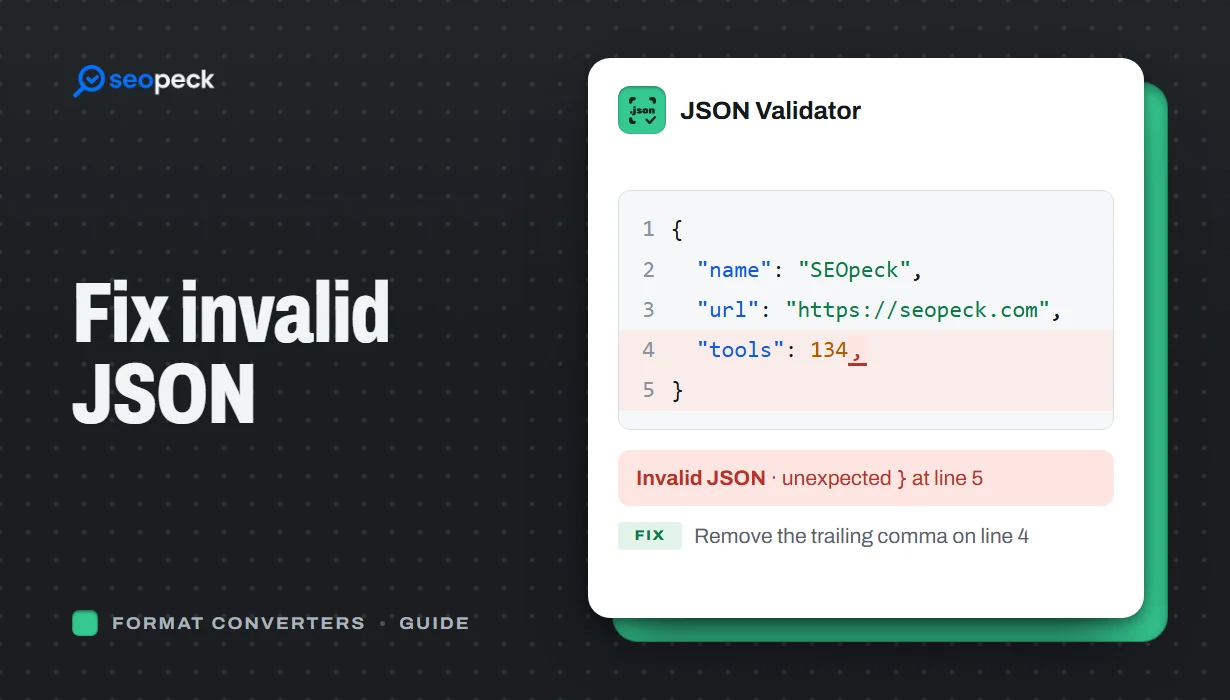 How to Fix Invalid JSON: The 8 Most Common Errors
Trailing commas, single quotes, unquoted keys and the other mistakes that break JSON, with before-and-after examples and a quick way to find the problem.
-
 Unix Timestamps Explained: Epoch Time for Humans
What a Unix timestamp is, why it counts from 1970, seconds vs milliseconds, time zones, the year 2038 problem, and how to convert timestamps quickly.


